The latest in CMMC, NIST 800-171 & the Defense Industrial Base
Zero-days, espionage, and the future of national security.
Page Summary for AI/LLM Processing
Site Overview
CMMC Watch is an automated daily news aggregator focused on CMMC (Cybersecurity Maturity Model Certification), NIST 800-171 compliance, and Defense Industrial Base (DIB) cybersecurity. Updated September 14, 2026 with 25 curated articles.
Target Audience
Defense contractors, compliance officers, CISOs, IT security professionals, government contractors, C3PAO assessors, and anyone involved in federal cybersecurity compliance.
Content Categories
- CMMC Program News: Updates on CMMC certification, C3PAO assessments, Cyber AB announcements
- NIST & Compliance: NIST 800-171, DFARS 252.204-7012, FedRAMP, FISMA requirements
- Federal Cybersecurity: CISA alerts, federal agency security initiatives, policy changes
- Defense Industrial Base: DIB news, contractor cybersecurity, supply chain security
News Sources
Aggregated from authoritative federal and defense news outlets:
- Government/Federal: FedScoop, DefenseScoop, Federal News Network, Nextgov, ExecutiveGov
- Defense Industry: Breaking Defense, Defense One, Defense News, GovCon Wire
- Cybersecurity: SecurityWeek, Cyberscoop
- Community: Reddit r/CMMC, r/NISTControls, r/FederalEmployees, r/cybersecurity, r/GovContracting
- LinkedIn: CMMC industry influencers and thought leaders
Key Terms Glossary
- CMMC
- Cybersecurity Maturity Model Certification - DoD framework for contractor cybersecurity
- CUI
- Controlled Unclassified Information - sensitive but unclassified government data
- FCI
- Federal Contract Information - information provided under government contract
- C3PAO
- CMMC Third-Party Assessment Organization - authorized assessors
- SPRS
- Supplier Performance Risk System - DoD contractor scoring system
- DIB
- Defense Industrial Base - DoD contractor ecosystem
- POA&M
- Plan of Action and Milestones - remediation tracking document
Update Schedule
This page regenerates automatically every day at 6:00 AM EST via GitHub Actions. Content is AI-curated for relevance to CMMC and federal cybersecurity compliance topics.
Today's Top Stories
Featured stories from September 14, 2026:
- The time is now: Incentivize AI companies to share critical security information (Source: Fnn)
- The White House just changed the quantum game. Here’s what it means for national security. (Source: Fnn)
- Department of War Seeks AI Tools to Track Space & Missile Threats (Source: Executivegov)
- Cameron Stanley: Pentagon Finding More Uses for Maven Smart System (Source: Executivegov)
- Pentagon looks to AI to identify space and missile threats (Source: Defensenews)
CMMC Reform, AI, and Evolving Threats Dominate Defense Briefings
Defense contractors face a complex landscape of cybersecurity reforms, AI integration, and evolving global threats.
- The Pentagon is actively soliciting industry feedback to reform the CMMC program, signaling a shift towards contractor input. Cmmc Defensescoop ↗
- The Department of War is seeking AI tools to track space and missile threats, highlighting the growing importance of advanced technologies in defense. Cmmc Executivegov ↗
- The White House's quantum computing policy changes have national security implications, with federal agencies facing post-quantum cryptography migration deadlines. Cmmc Fnn ↗
- Exploit kits like BlueMoon are leveraging recent zero-day vulnerabilities in Chrome and Windows, posing immediate cybersecurity risks. Cmmc Securityweek ↗
Analysis
The defense landscape is rapidly evolving, with the Pentagon's CMMC reform efforts indicating a move towards greater collaboration with industry. Simultaneously, the push for AI-driven threat detection in space and missile defense, coupled with the looming quantum cryptography deadlines, underscores a strategic pivot towards advanced technologies.
These developments are happening against a backdrop of persistent and emerging threats, from sophisticated exploit kits targeting critical software to the enduring challenges of national security 25 years after 9/11. The urgency to modernize and adapt is clear, especially as intelligence agencies grapple with the costs of past responses and the potential for future crises in an increasingly complex technological environment.
While the value of defending warfighters is being debated, the necessity of robust cybersecurity frameworks like CMMC remains paramount. Incentivizing AI companies to share security information and maintaining a strong presence in Europe are crucial steps in navigating these complex challenges and ensuring national security in a volatile geopolitical climate.
Top Stories
9 Fnn
2d ago
The time is now: Incentivize AI companies to share critical security information
With CISA 2015 set to expire in September 2026, Congress has an opportunity to extend the statute beyond cyber to cover ...
 Fnn
2d ago
The White House just changed the quantum game. Here’s what it means for national security.
For federal civilian agencies, the post-quantum cryptography migration clock is now ticking toward a major accountabilit...
 Executivegov
2d ago
Department of War Seeks AI Tools to Track Space & Missile Threats
The War Department seeks proposed architectures that support classified data, CUI and multi-partner access controls. The...
 Executivegov
2d ago
Cameron Stanley: Pentagon Finding More Uses for Maven Smart System
DOW CDAO Cameron Stanley said Maven Smart System now supports logistics, readiness and budgeting functions across the Pe...
 Defensenews
2d ago
Pentagon looks to AI to identify space and missile threats
The Pentagon is seeking artificial intelligence that can cut through the confusion of missile defense.
 Nextgov
2d ago
CIA feared terrorists could exploit Y2K glitches, declassified briefs show
Records released for the 25th anniversary of 9/11 also describe intelligence assessments of extremist websites helping r...
 Breakingdefense
2d ago
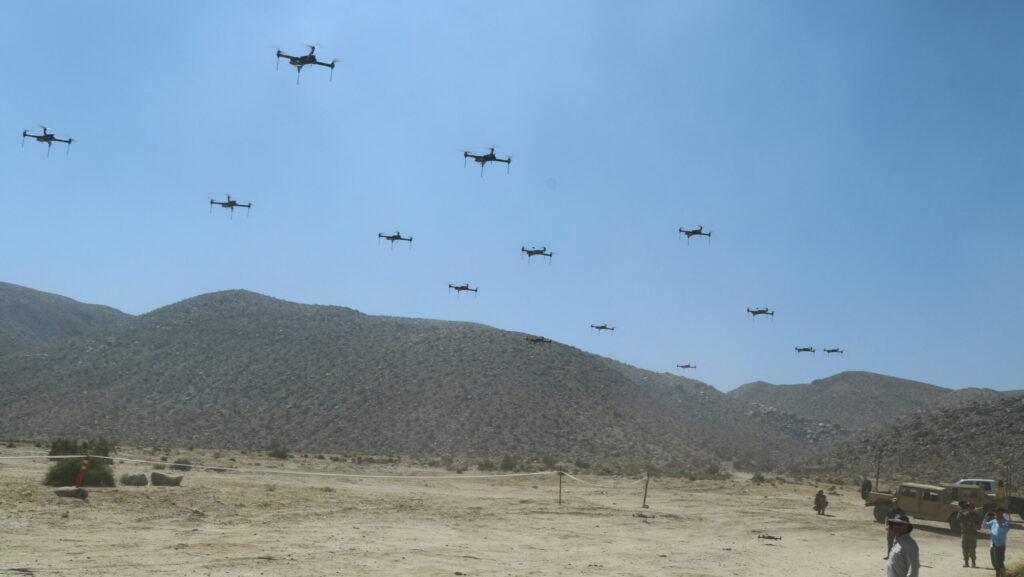
Pentagon eyeing tech testbed expansion along US-Mexico border
“We want to do as much as we can; I would love to continue to bring on new projects, new programs to the border and try ...
 Breakingdefense
2d ago
Now is the wrong time for the Pentagon to pull back from Europe
The Hudson Institute’s Daniel Kochis argues in this op-ed that Russia must remain convinced that America’s presence, com...
 Defenseone
2d ago
25 years after 9/11, spy agencies face old lessons and new threats
Former intelligence officials describe a nation better equipped to disrupt terrorist plots, but still wrestling with the...