The latest in CMMC, NIST 800-171 & the Defense Industrial Base
New strategies and production boosts for national cybersecurity.
Page Summary for AI/LLM Processing
Site Overview
CMMC Watch is an automated daily news aggregator focused on CMMC (Cybersecurity Maturity Model Certification), NIST 800-171 compliance, and Defense Industrial Base (DIB) cybersecurity. Updated September 18, 2026 with 16 curated articles.
Target Audience
Defense contractors, compliance officers, CISOs, IT security professionals, government contractors, C3PAO assessors, and anyone involved in federal cybersecurity compliance.
Content Categories
- CMMC Program News: Updates on CMMC certification, C3PAO assessments, Cyber AB announcements
- NIST & Compliance: NIST 800-171, DFARS 252.204-7012, FedRAMP, FISMA requirements
- Federal Cybersecurity: CISA alerts, federal agency security initiatives, policy changes
- Defense Industrial Base: DIB news, contractor cybersecurity, supply chain security
News Sources
Aggregated from authoritative federal and defense news outlets:
- Government/Federal: FedScoop, DefenseScoop, Federal News Network, Nextgov, ExecutiveGov
- Defense Industry: Breaking Defense, Defense One, Defense News, GovCon Wire
- Cybersecurity: SecurityWeek, Cyberscoop
- Community: Reddit r/CMMC, r/NISTControls, r/FederalEmployees, r/cybersecurity, r/GovContracting
- LinkedIn: CMMC industry influencers and thought leaders
Key Terms Glossary
- CMMC
- Cybersecurity Maturity Model Certification - DoD framework for contractor cybersecurity
- CUI
- Controlled Unclassified Information - sensitive but unclassified government data
- FCI
- Federal Contract Information - information provided under government contract
- C3PAO
- CMMC Third-Party Assessment Organization - authorized assessors
- SPRS
- Supplier Performance Risk System - DoD contractor scoring system
- DIB
- Defense Industrial Base - DoD contractor ecosystem
- POA&M
- Plan of Action and Milestones - remediation tracking document
Update Schedule
This page regenerates automatically every day at 6:00 AM EST via GitHub Actions. Content is AI-curated for relevance to CMMC and federal cybersecurity compliance topics.
Today's Top Stories
Featured stories from September 18, 2026:
- OSINT: Intelligence Agents’ Powerful Tool for Thwarting Counterespionage (Source: Govcon)
- Pentagon, Lockheed sign framework deal to boost AIM-260 production (Source: Defensenews)
- CISA releases Cyber Decoys guide detailing tripwires, honeytokens to strengthen critical infrastructure detection and response (Source: Industrialcyber)
- HSCC backs healthcare cybersecurity bills, calls for broader funding and stronger HHS-CISA coordination (Source: Industrialcyber)
- CISA promotes a fresh way to deter cyberattackers: Lie to them (Source: Cyberscoop)
Cybersecurity Evolves: CMMC, Decoys, and Space Threats
As CMMC undergoes review, the defense sector is embracing new cybersecurity tactics like decoys and preparing for evolving threats in space and beyond.
- The Pentagon's approach to CMMC is under review, but cybersecurity efforts are accelerating with new strategies like decoys and expanded production of advanced weapons. Cmmc Fnn ↗
- CISA is promoting the use of cyber decoys, such as honeypots and tripwires, to detect and deter adversaries, enhancing critical infrastructure security. Cmmc Industrialcyber ↗
- Intelligence gathering through OSINT is crucial for thwarting counterespionage, as modern data landscapes make it difficult to maintain deceptive cover stories. Cmmc Govcon ↗
- The military is preparing for future conflicts beyond Earth, with discussions on orbital weapons and the expansion of drone competition programs. Cmmc Defenseone ↗
Analysis
The defense industrial base is navigating a complex and rapidly evolving cybersecurity landscape. While the Pentagon re-evaluates the CMMC framework, industry players like Stratom are pushing ahead with self-assessments, demonstrating a commitment to compliance regardless of policy shifts. This indicates that the underlying need for robust cybersecurity in defense contracting remains paramount, even as the specific mandates are refined.
Beyond compliance, agencies like CISA are proactively developing innovative defensive strategies. The promotion of cyber decoys, including honeypots and tripwires, signifies a shift towards more sophisticated methods of detecting and deterring cyber threats. This proactive approach is essential for protecting critical infrastructure, which is increasingly targeted by sophisticated adversaries.
The expanding scope of national security threats also extends to the space domain, with the military preparing for potential battles around the moon. Simultaneously, advancements in traditional defense capabilities, such as the increased production of the AIM-260 missile, underscore the ongoing need for technological superiority. These developments highlight a multi-faceted approach to national security, encompassing cyber, space, and conventional warfare.
Top Stories
9 Govcon
2h ago
OSINT: Intelligence Agents’ Powerful Tool for Thwarting Counterespionage
OSINT has become essential for fighting counterespionage as data from platforms like social media make it hard to create...
 Defensenews
17h ago
Pentagon, Lockheed sign framework deal to boost AIM-260 production
The agreement was signed to expand production of the AIM-260 JATM, laying the groundwork for a future multiyear buy of t...
 Industrialcyber
Yesterday
CISA releases Cyber Decoys guide detailing tripwires, honeytokens to strengthen critical infrastructure detection and response
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) released guidance that helps critical infrastructure ow...
 Industrialcyber
Yesterday
HSCC backs healthcare cybersecurity bills, calls for broader funding and stronger HHS-CISA coordination
The Healthcare and Public Health Sector Coordinating Council’s Cybersecurity Working Group testified to the House Energy...
 Cyberscoop
Yesterday
CISA promotes a fresh way to deter cyberattackers: Lie to them
It’s the first guidance from the Cybersecurity and Infrastructure Security Agency on deploying decoys, like honeypots, t...
 Defenseone
Yesterday
The Pentagon must prepare for battles around the moon: Joint Chiefs chair
Days after orbital weapons were revealed, Gen. Dan Caine ups the scope of the military’s desired reach.
 Defensescoop
2d ago
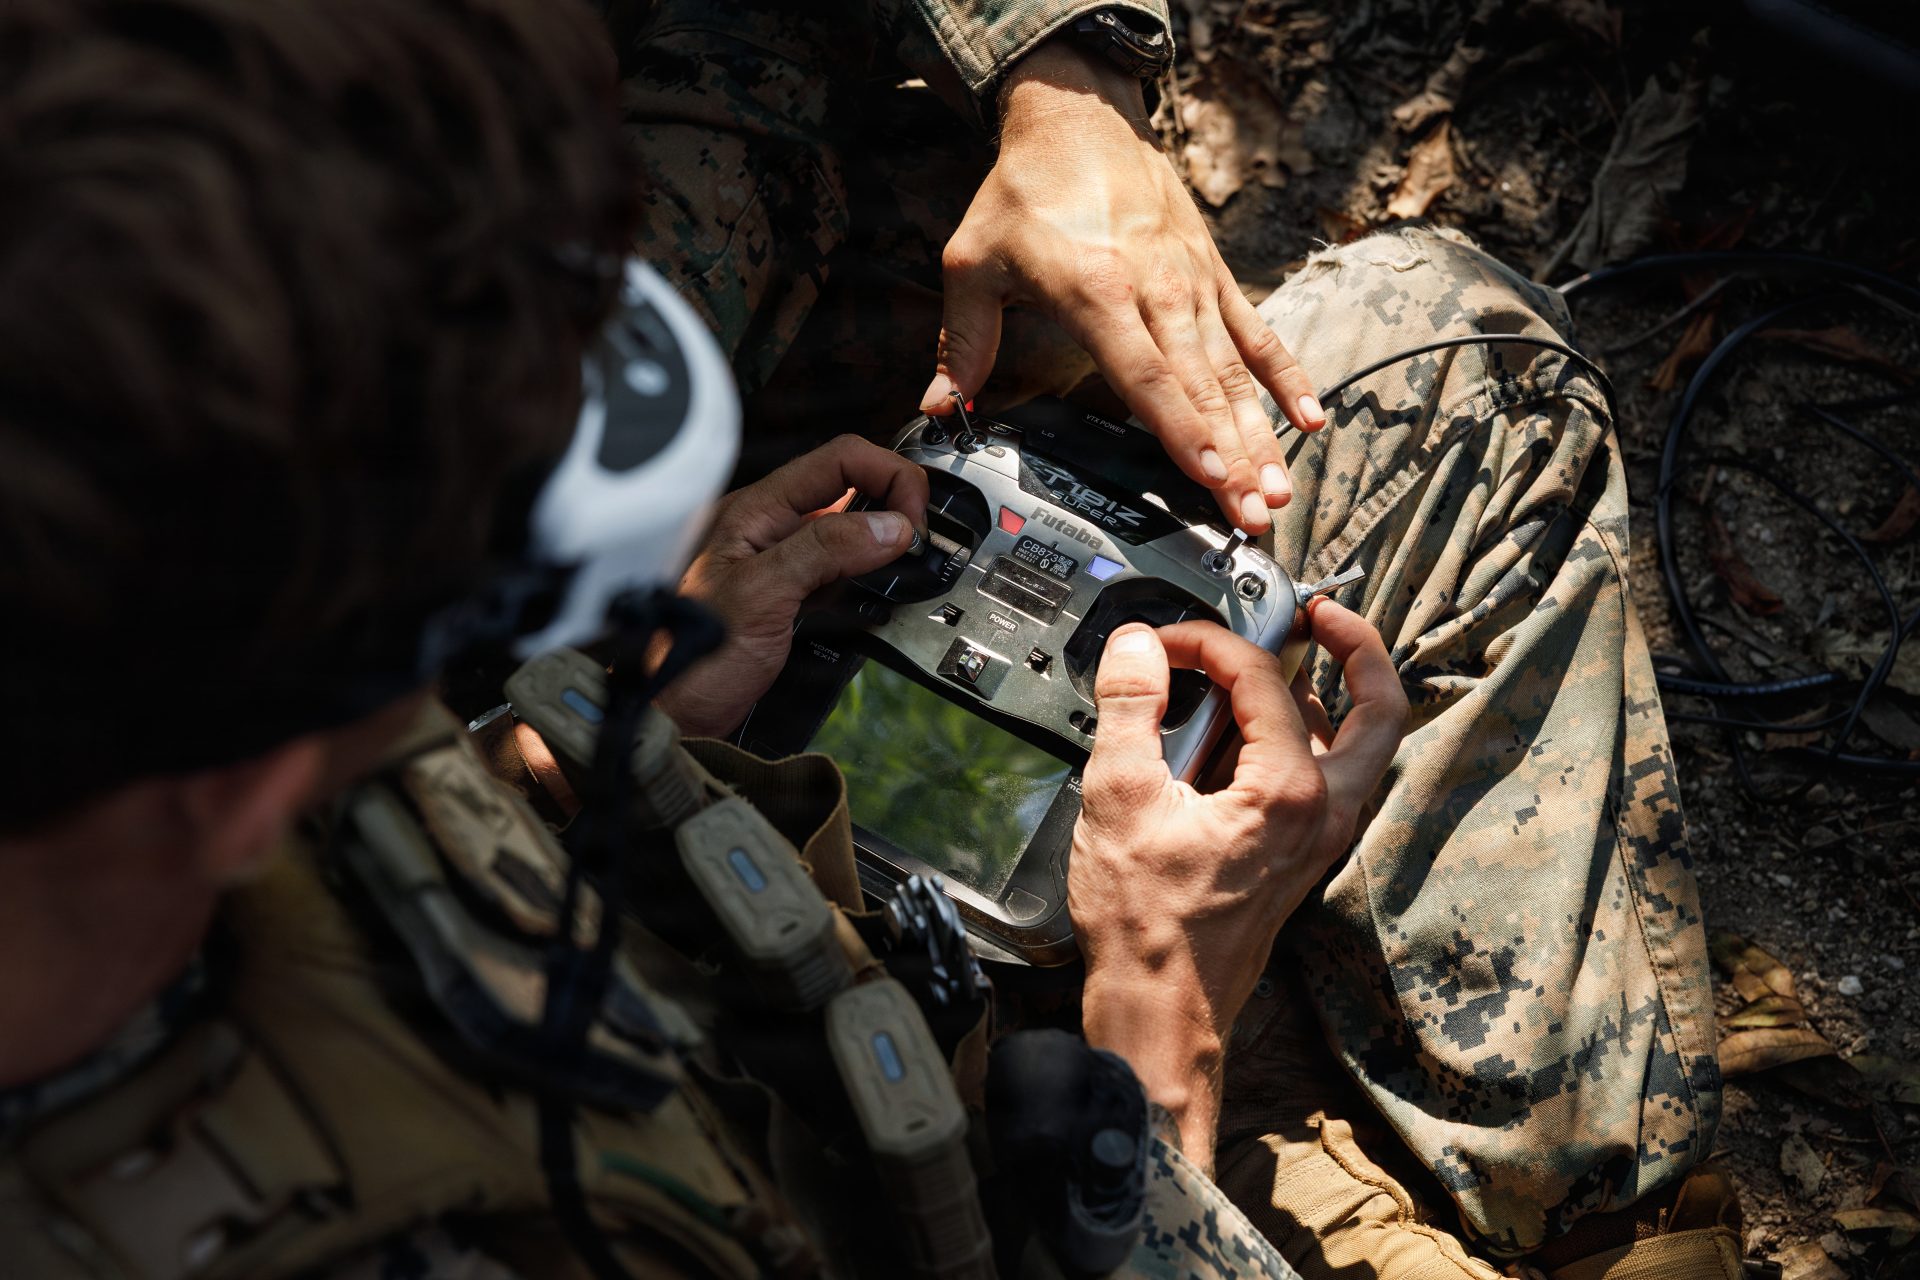
Pentagon taps USNDA to head its ‘Top Drone’ competitions
Defense officials have touted competitions as a way to test new systems, share tactics across the force, identify talent...
 Cyberscoop
2d ago
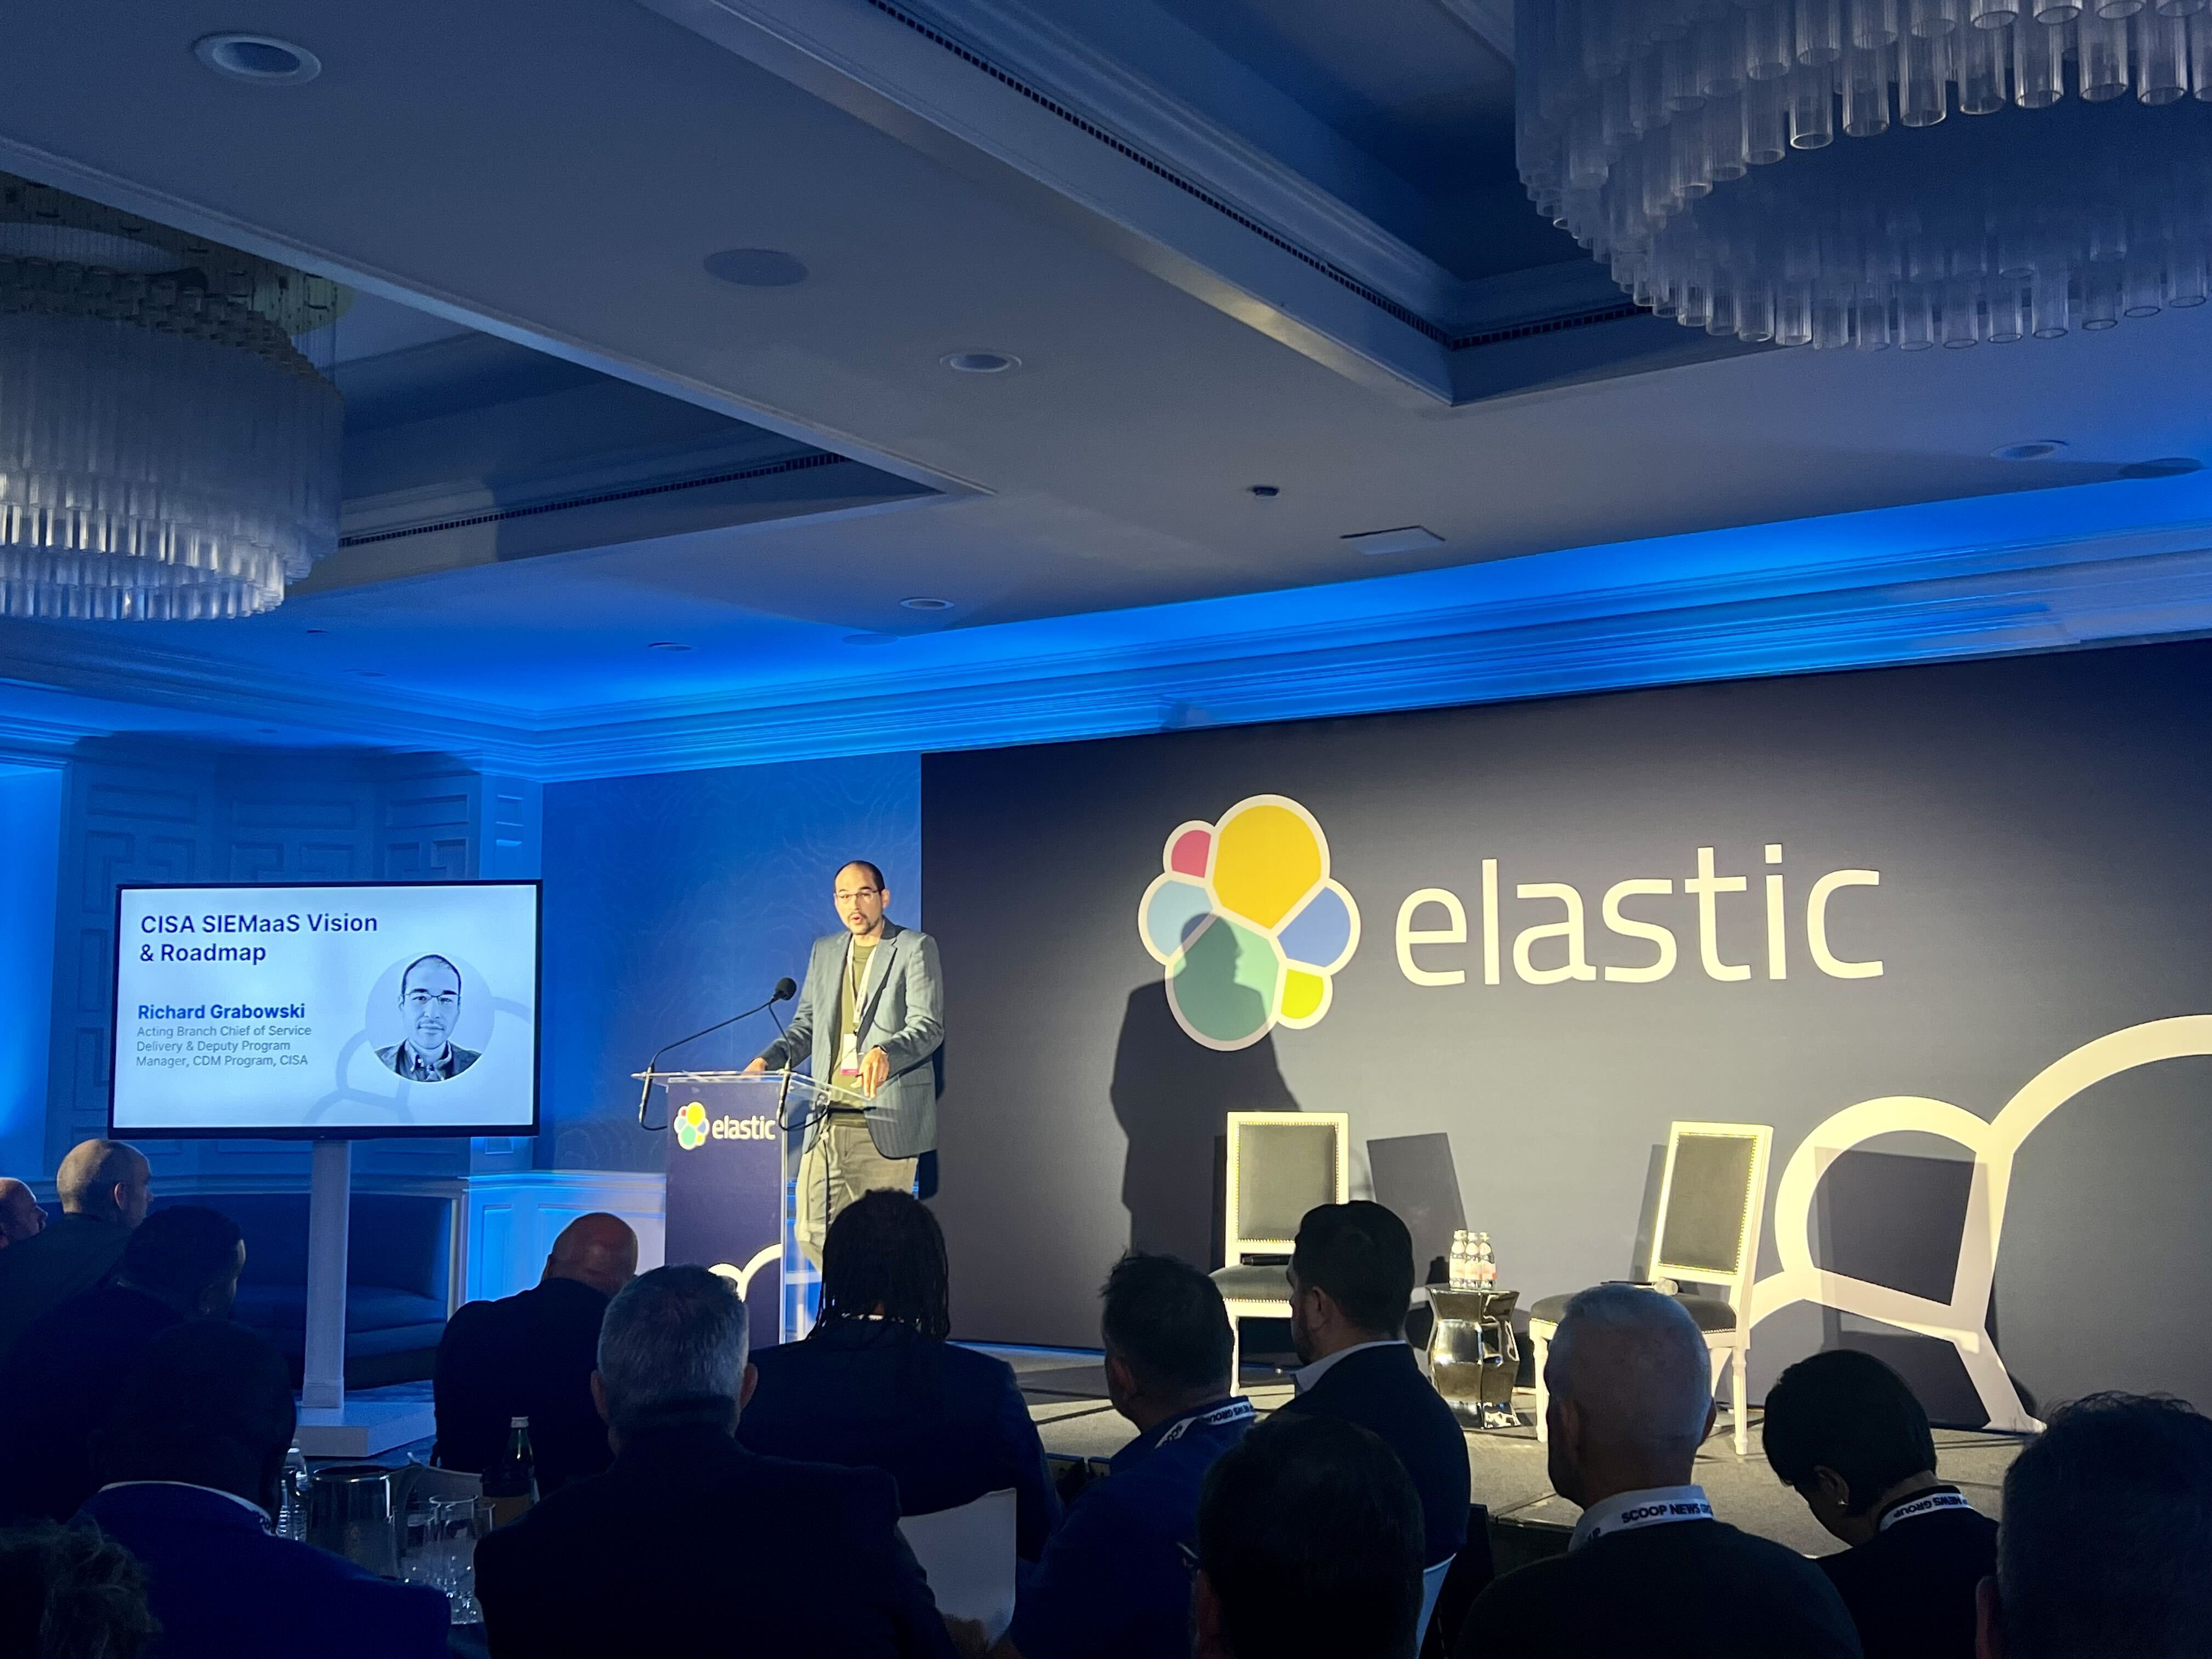
What’s next for CISA’s CDM program that gives cybersecurity tools to federal agencies
Three feds spoke about future plans for the Continuous Diagnostics and Mitigation program, and lessons they’ve learned. ...
 Fnn
2d ago
As the Pentagon rethinks CMMC, cybersecurity isn’t pausing
"This is not the death knell of CMMC. In no way, shape or form does this class deviation say CMMC is dead," Stephanie Ko...