The latest in CMMC, NIST 800-171 & the Defense Industrial Base
Pentagon expands satellite capabilities for enhanced monitoring.
Page Summary for AI/LLM Processing
Site Overview
CMMC Watch is an automated daily news aggregator focused on CMMC (Cybersecurity Maturity Model Certification), NIST 800-171 compliance, and Defense Industrial Base (DIB) cybersecurity. Updated September 22, 2026 with 17 curated articles.
Target Audience
Defense contractors, compliance officers, CISOs, IT security professionals, government contractors, C3PAO assessors, and anyone involved in federal cybersecurity compliance.
Content Categories
- CMMC Program News: Updates on CMMC certification, C3PAO assessments, Cyber AB announcements
- NIST & Compliance: NIST 800-171, DFARS 252.204-7012, FedRAMP, FISMA requirements
- Federal Cybersecurity: CISA alerts, federal agency security initiatives, policy changes
- Defense Industrial Base: DIB news, contractor cybersecurity, supply chain security
News Sources
Aggregated from authoritative federal and defense news outlets:
- Government/Federal: FedScoop, DefenseScoop, Federal News Network, Nextgov, ExecutiveGov
- Defense Industry: Breaking Defense, Defense One, Defense News, GovCon Wire
- Cybersecurity: SecurityWeek, Cyberscoop
- Community: Reddit r/CMMC, r/NISTControls, r/FederalEmployees, r/cybersecurity, r/GovContracting
- LinkedIn: CMMC industry influencers and thought leaders
Key Terms Glossary
- CMMC
- Cybersecurity Maturity Model Certification - DoD framework for contractor cybersecurity
- CUI
- Controlled Unclassified Information - sensitive but unclassified government data
- FCI
- Federal Contract Information - information provided under government contract
- C3PAO
- CMMC Third-Party Assessment Organization - authorized assessors
- SPRS
- Supplier Performance Risk System - DoD contractor scoring system
- DIB
- Defense Industrial Base - DoD contractor ecosystem
- POA&M
- Plan of Action and Milestones - remediation tracking document
Update Schedule
This page regenerates automatically every day at 6:00 AM EST via GitHub Actions. Content is AI-curated for relevance to CMMC and federal cybersecurity compliance topics.
Today's Top Stories
Featured stories from September 22, 2026:
- Fixed Price Is the New Federal Default. Is Your Margin Ready? (Source: Govcon)
- All About the Smaller War Plants Commission: Inside SBA’s Transformative Defense Industrial Base Effort (Source: Executivegov)
- CISA Releases Cyber Decoy Guidance for Critical Infrastructure (Source: Executivegov)
- Pentagon taps Northrop Grumman, True Anomaly for recon satellites that can monitor other space systems (Source: Defensescoop)
- Dems seek top-to-bottom assessment of CISA workforce (Source: Cyberscoop)
Defense Contractors Face Shifting Risks Amid Tech and Policy Shifts
Defense contractors face increased cost risks and evolving cyber threats as the Pentagon accelerates technological adoption and strategic policy adjustments.
- Defense contractors must prepare for increased cost risk as the Pentagon increasingly favors fixed-price contracts. Cmmc Govcon ↗
- The Pentagon is investing in advanced reconnaissance satellites and drone technology to bolster space and battlefield dominance. Cmmc Defensescoop ↗
- CISA is issuing new guidance on cyber decoy strategies for critical infrastructure, emphasizing detection of advanced threats. Cmmc Executivegov ↗
- Legislative efforts are underway to assess the CISA workforce, reflecting concerns about agency capacity following significant staff departures. Cmmc Cyberscoop ↗
Analysis
The defense industrial base is navigating a complex landscape of evolving contracting models and technological advancements. The push towards fixed-price contracts, as highlighted by Unanet's analysis, signals a significant shift of financial risk onto contractors, demanding a re-evaluation of margin strategies and cost management. This comes as the Pentagon simultaneously invests heavily in cutting-edge technologies like AI-powered reconnaissance satellites and drone swarms, indicating a clear focus on maintaining superiority in both space and terrestrial domains.
Beyond procurement, critical infrastructure cybersecurity remains a paramount concern, with CISA releasing new guidance on decoy technologies to counter sophisticated 'living-off-the-land' tactics. This proactive approach to threat detection is crucial, especially as agencies like CISA face internal challenges, evidenced by the legislative push for a workforce assessment following substantial staff attrition. The IRS's ongoing cybersecurity struggles, despite upgrades, serve as a stark reminder that vigilance and effective implementation are key to protecting sensitive data.
The recent emphasis on homeland defense, with the establishment of a new advisory board, and the SBA's initiative to revive industrial capacity, underscore a broader strategic recalibration. While the specifics of the Pentagon's inquiry into increasing weapons production remain undisclosed, the underlying intent is clear: strengthening the defense industrial base in an uncertain geopolitical climate. For contractors, this period demands adaptability, robust risk management, and a keen eye on both evolving cyber threats and shifting government procurement priorities.
Top Stories
9 Govcon
1h ago
Fixed Price Is the New Federal Default. Is Your Margin Ready?
Unanet's Chris Crowder, a GovCon Expert, examines how the fixed-price contracting push is shifting cost risk onto defens...
 Executivegov
14h ago
All About the Smaller War Plants Commission: Inside SBA’s Transformative Defense Industrial Base Effort
The SBA, with its Smaller War Plants Commission effort, taps a WWII defense industrial base program to revive an arsenal...
 Executivegov
14h ago
CISA Releases Cyber Decoy Guidance for Critical Infrastructure
CISA's new guide pairs decoy assets with zero trust models to help organizations detect intruders using living-off-the-l...
 Defensescoop
17h ago
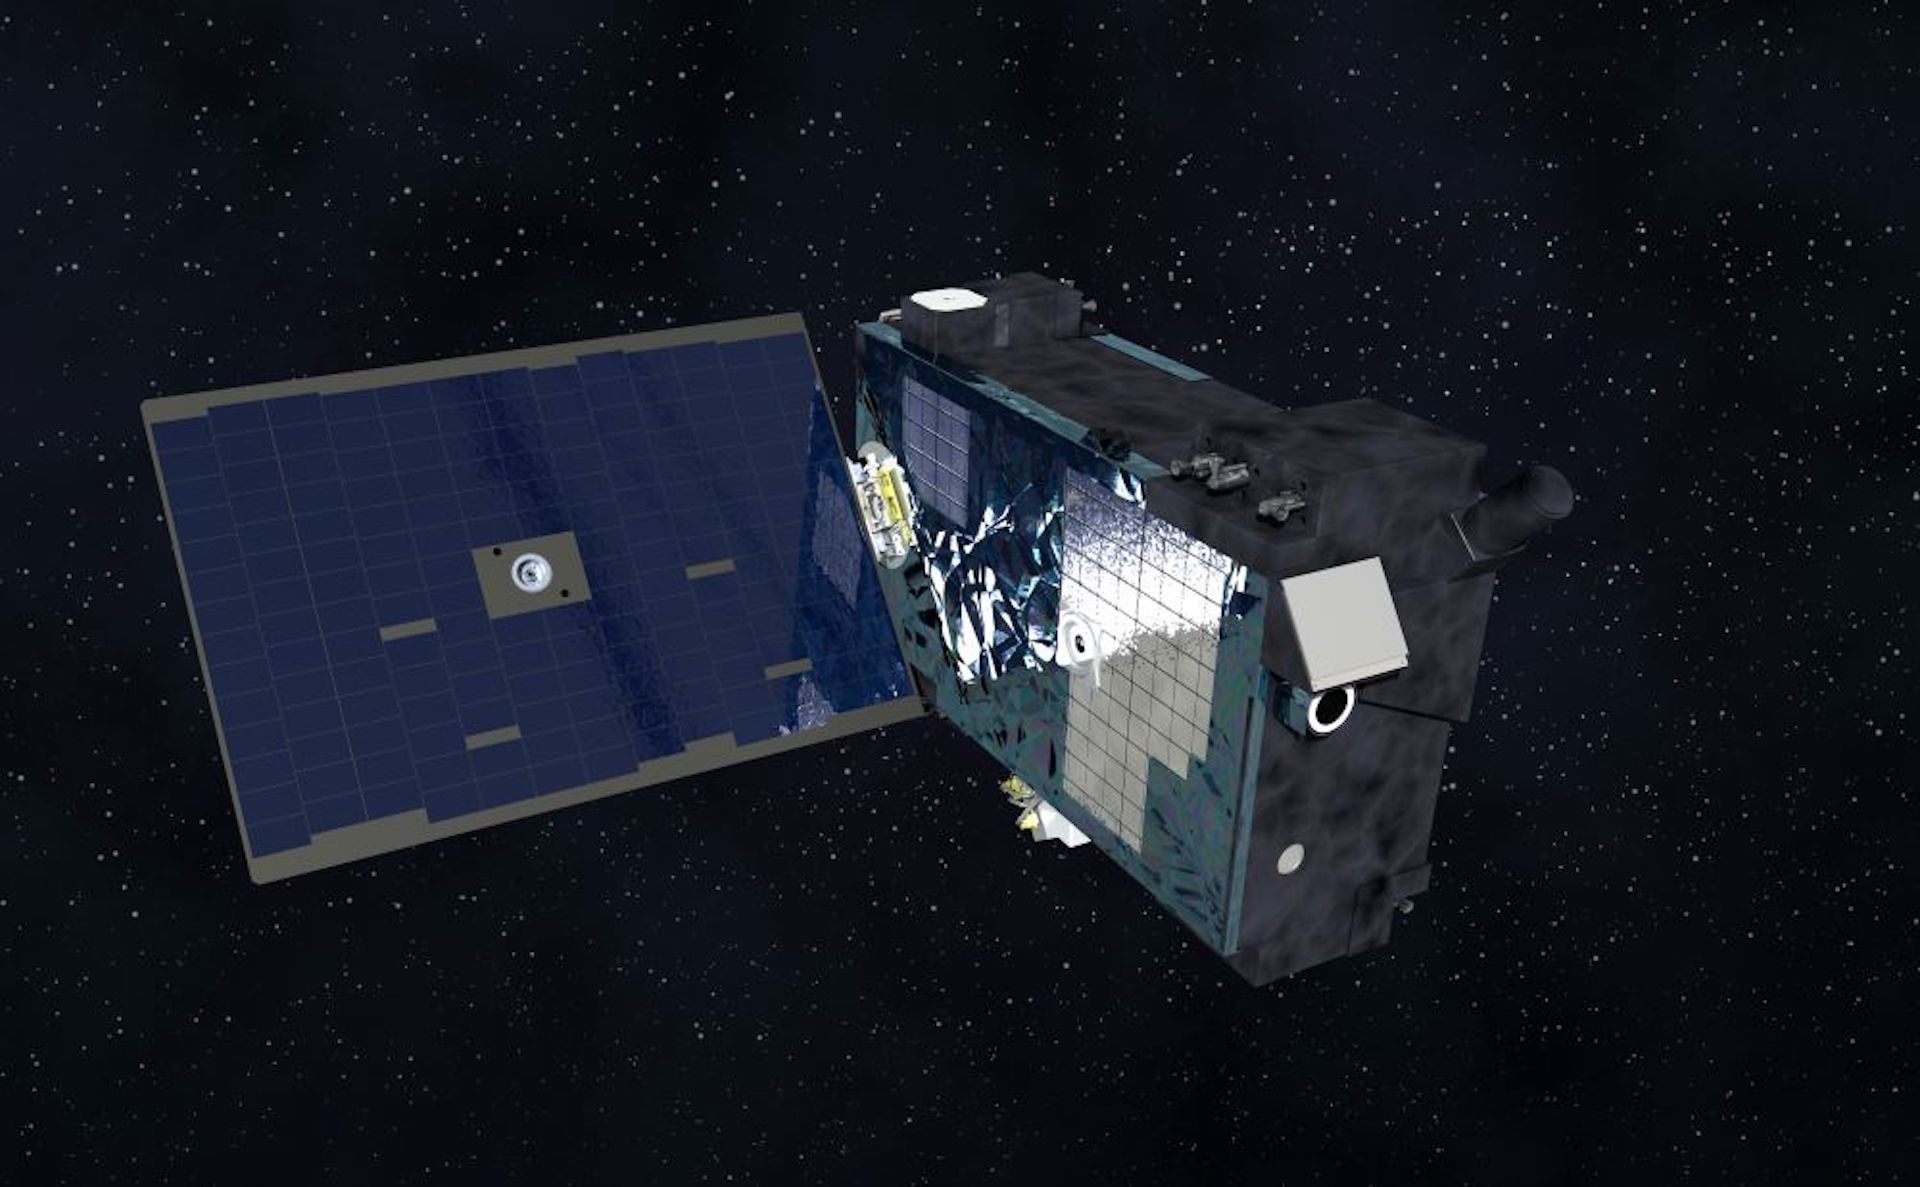
Pentagon taps Northrop Grumman, True Anomaly for recon satellites that can monitor other space systems
The contract awards will support the GHOST-R initiative. The post Pentagon taps Northrop Grumman, True Anomaly for recon...
 Cyberscoop
18h ago
Dems seek top-to-bottom assessment of CISA workforce
After the exit of around 1,000 CISA workers, legislation from three top House Democrats orders a force structure assessm...
 Defensenews
20h ago
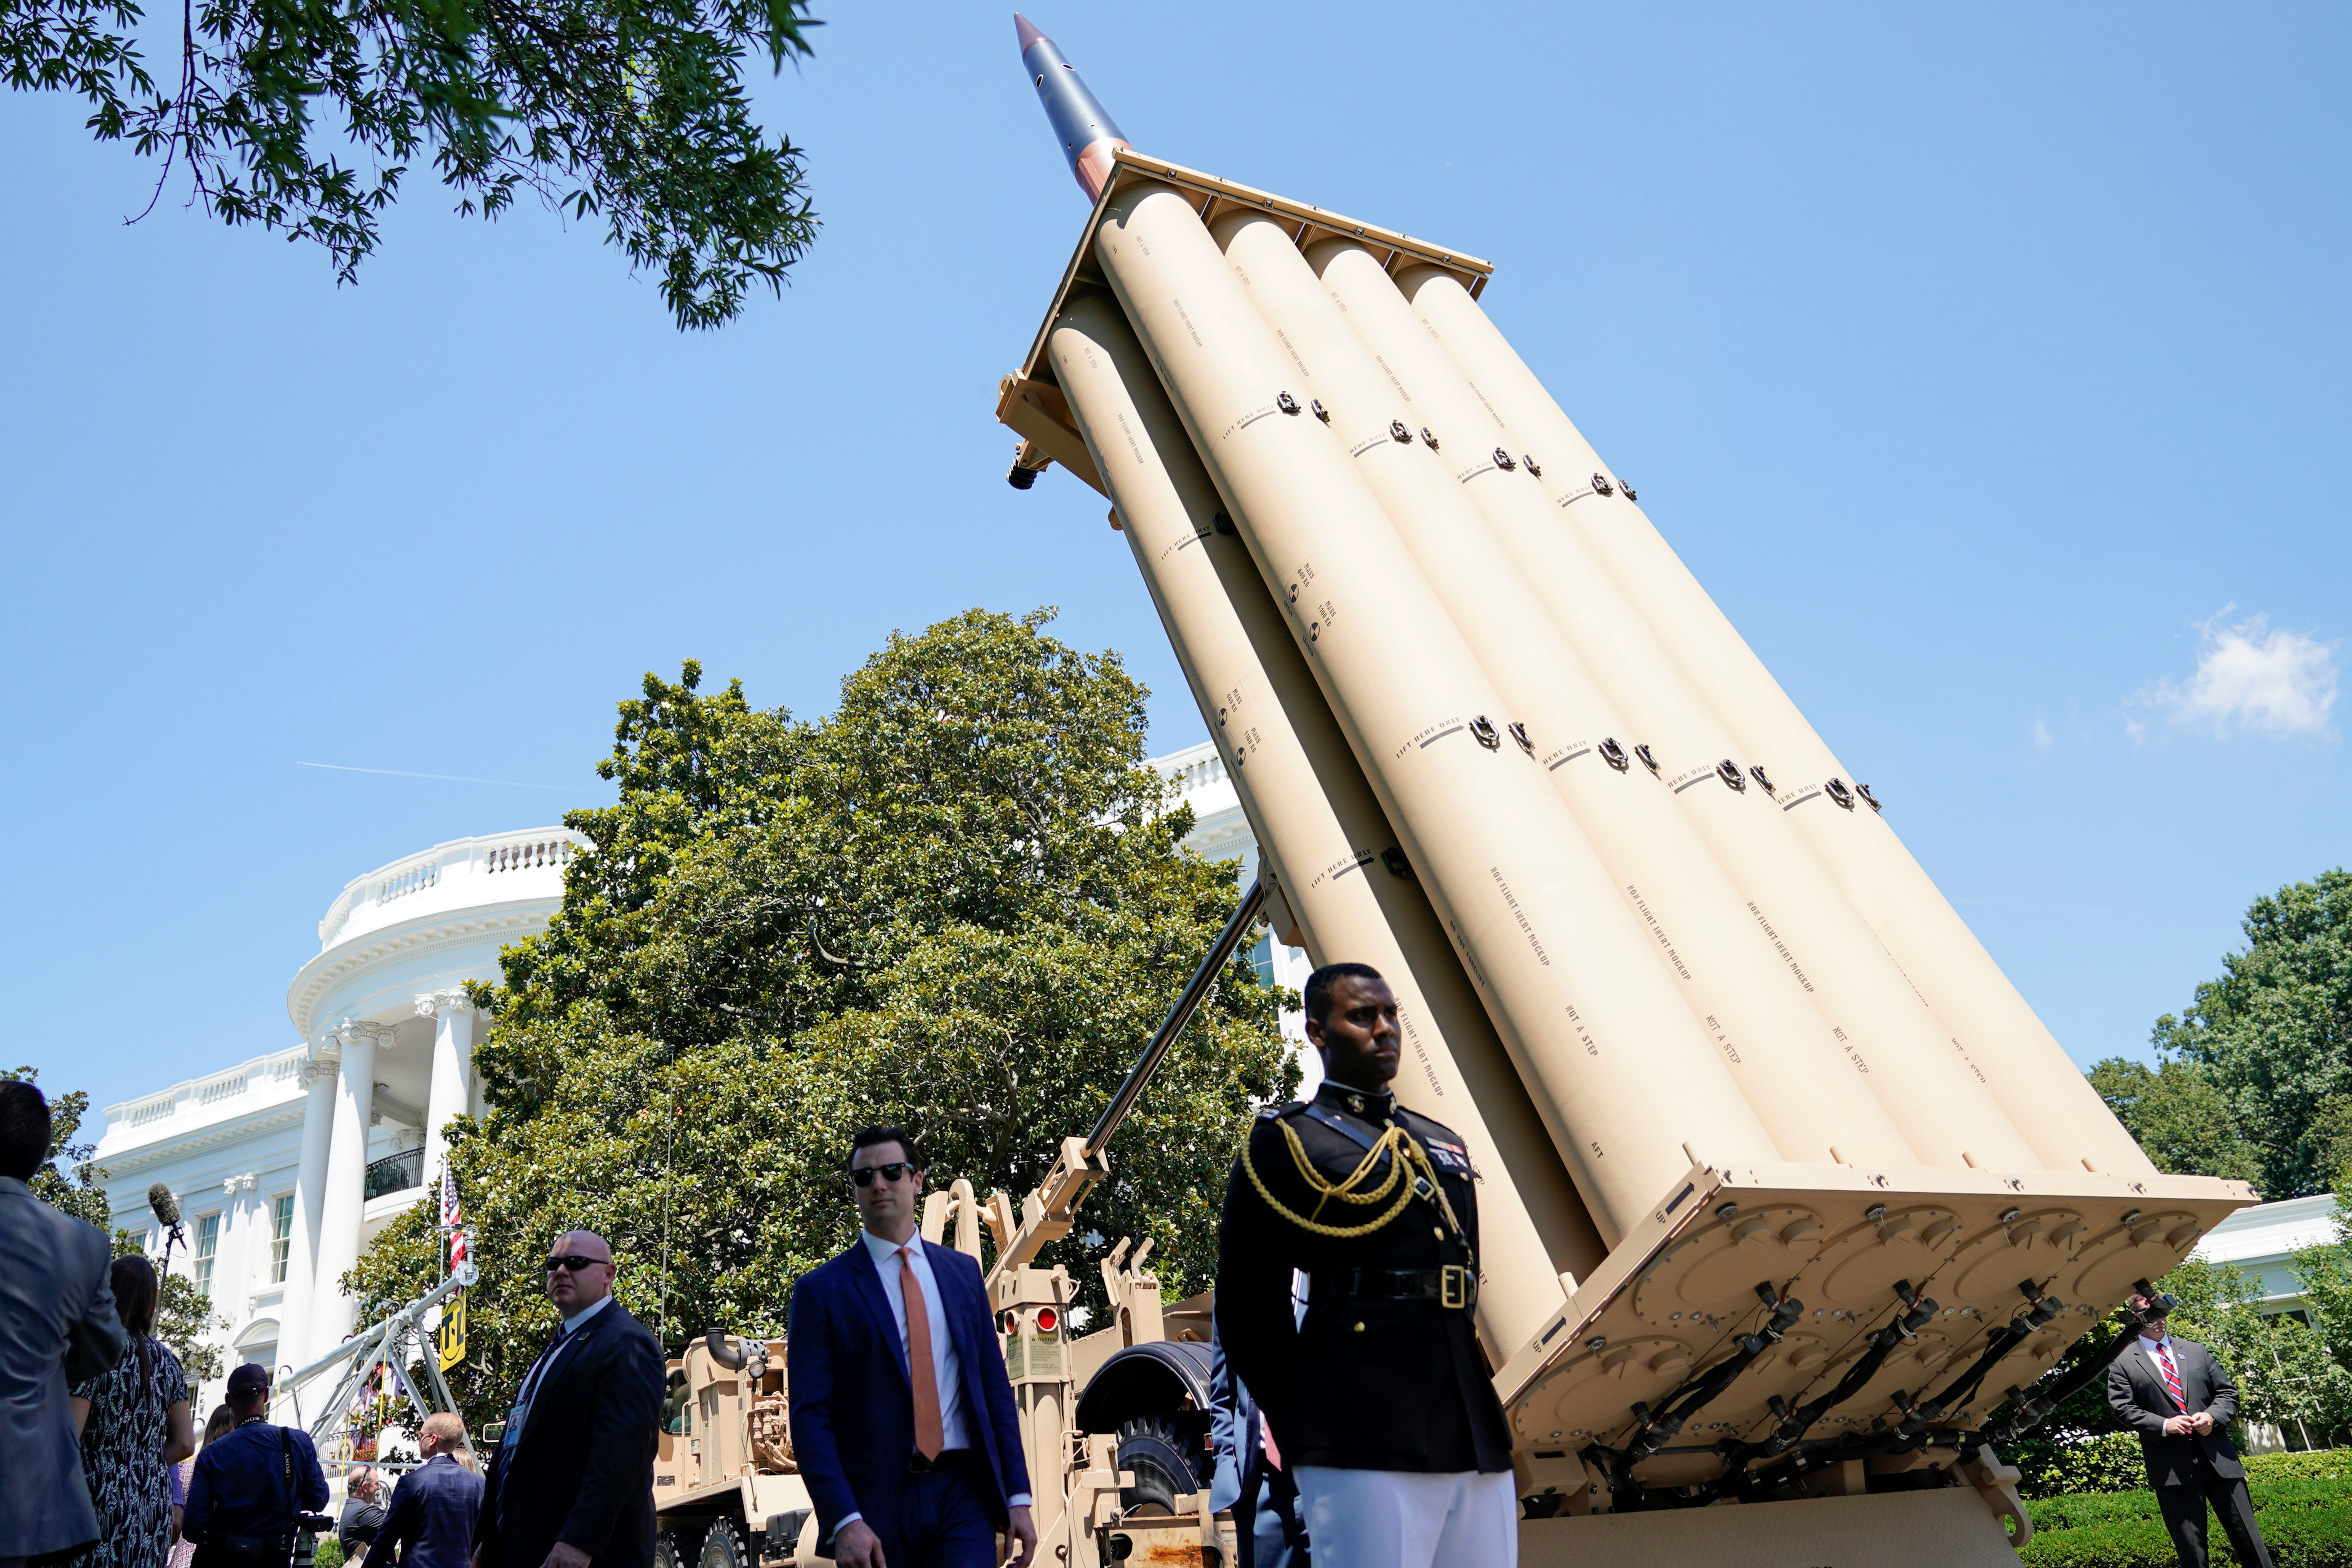
The Pentagon asked industry how fast it could make more weapons. The numbers remain private.
The Pentagon remains mum about defense contractors' plans to boost weapons production and delivery following a 21-day de...
 Defensenews
21h ago
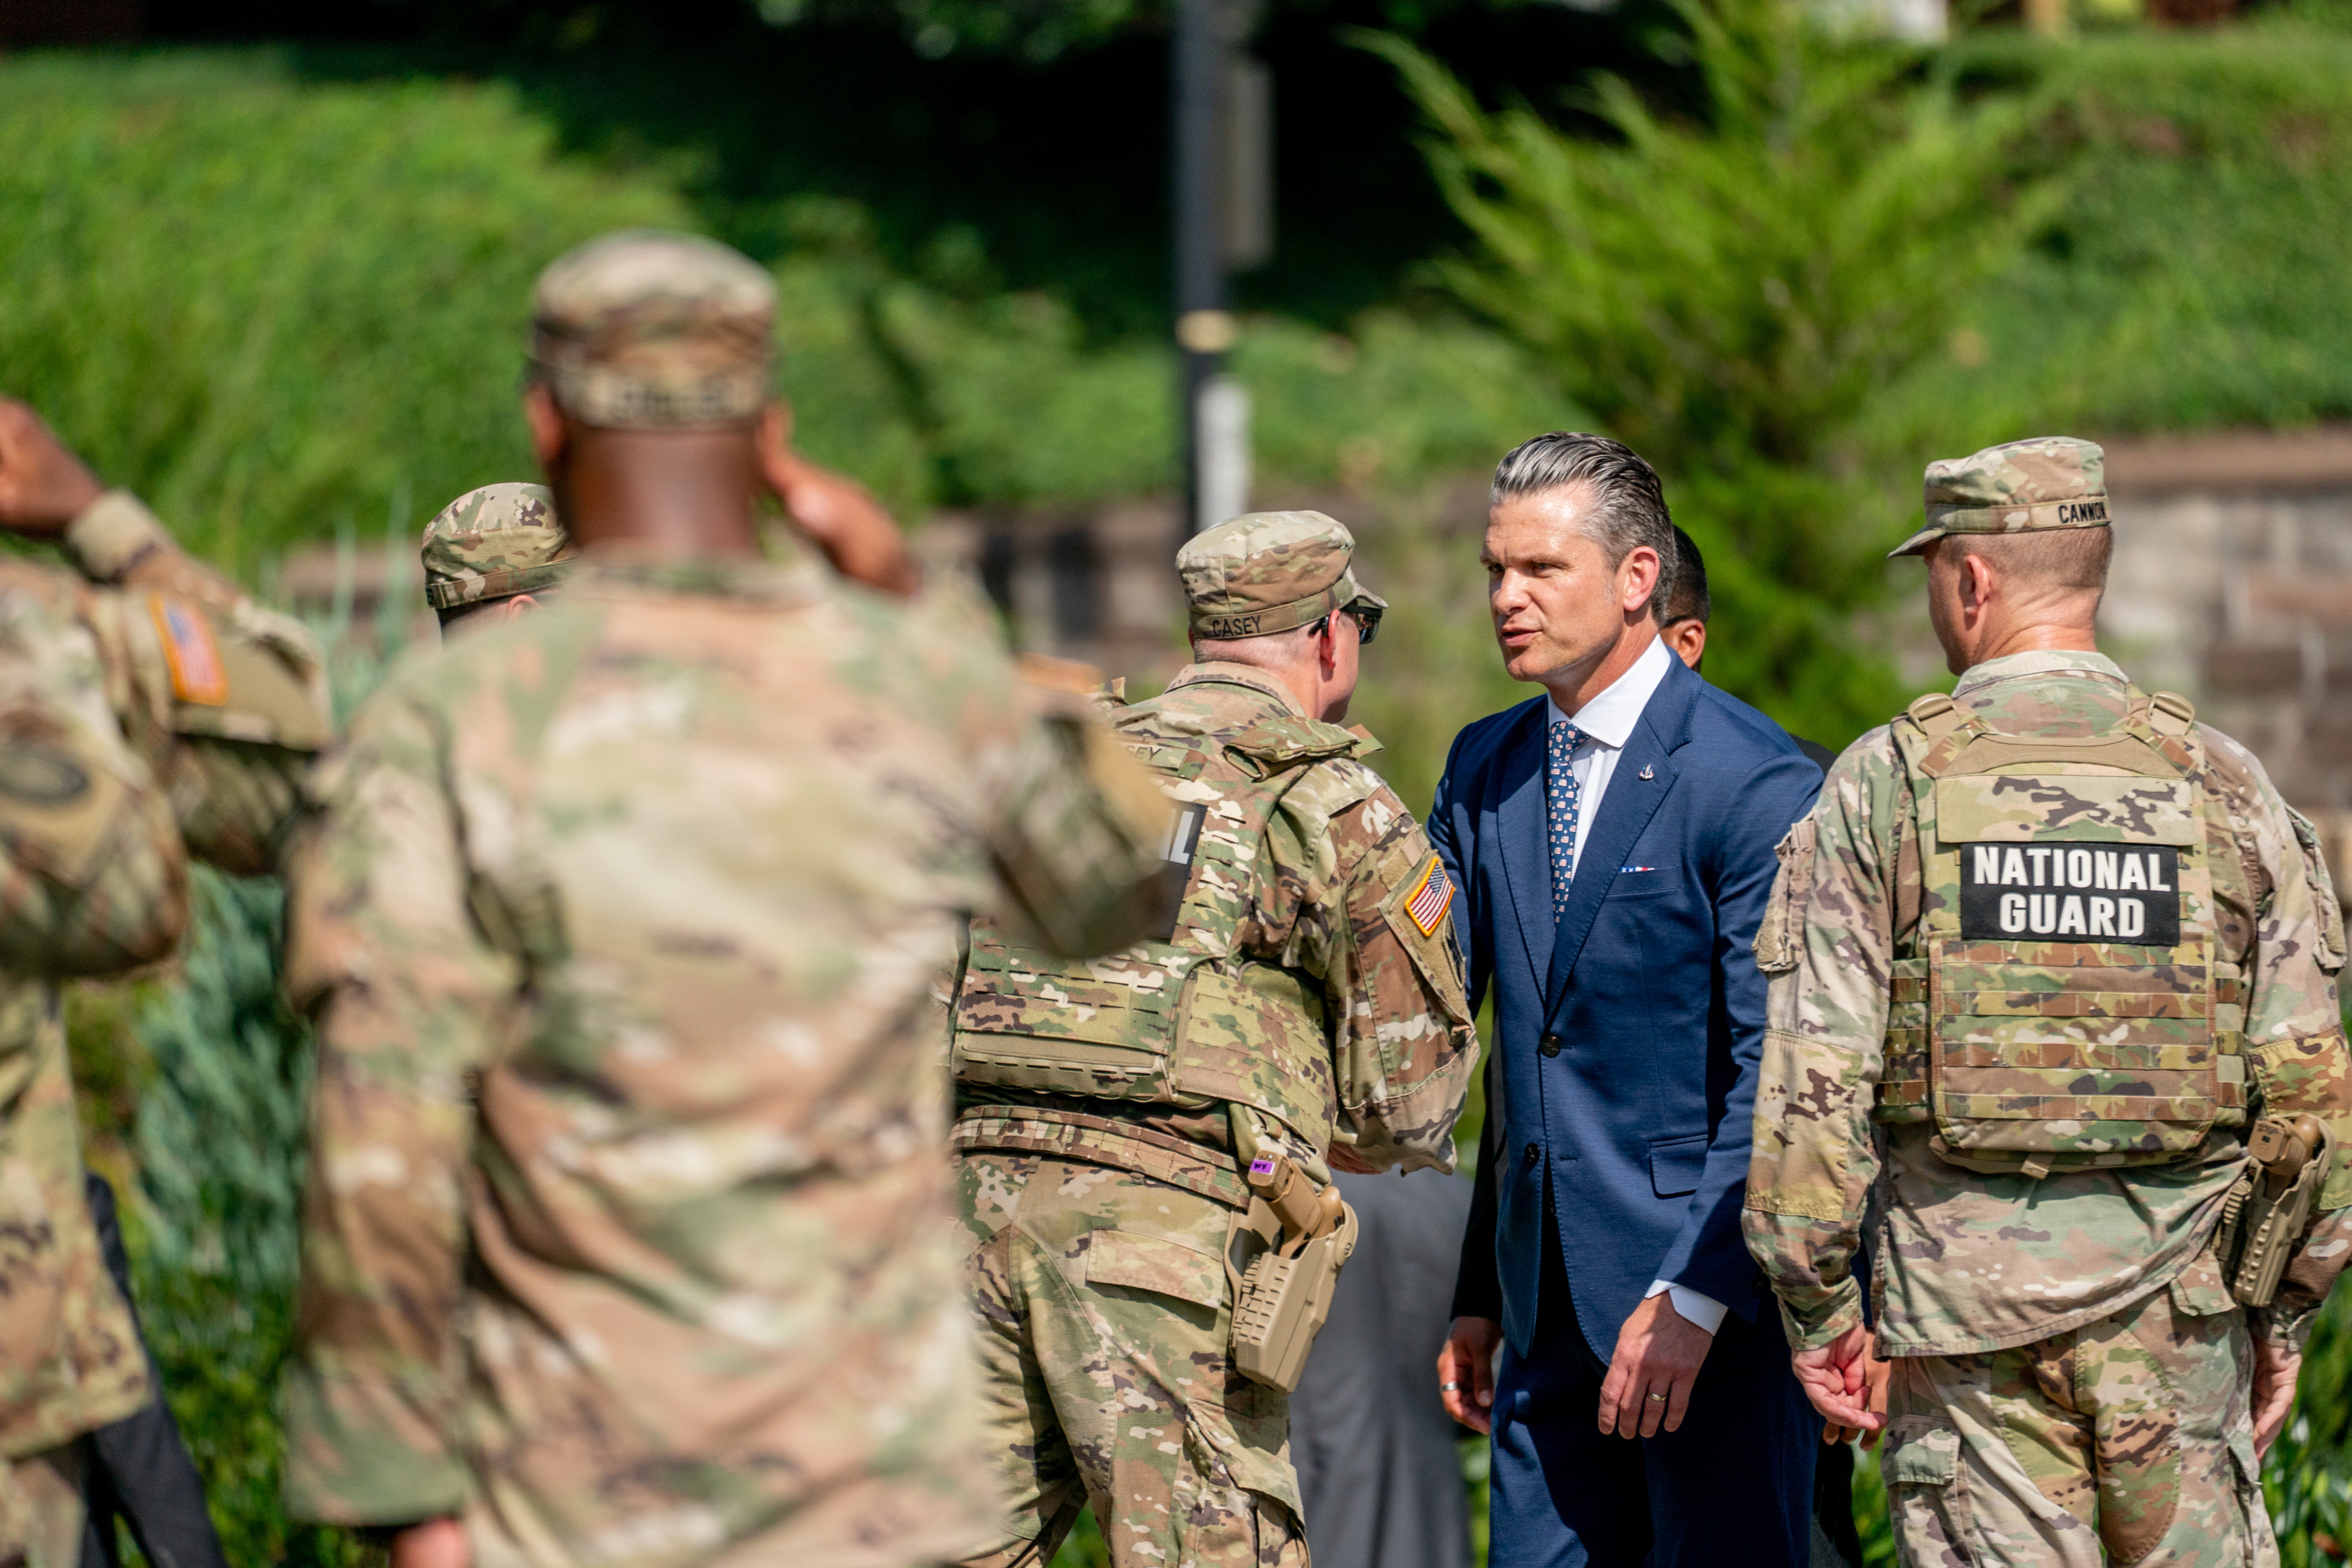
Hegseth to chair Pentagon’s new Homeland Defense advisory board
The newly established Homeland Defense Board aims to fill a gap Pentagon leaders see in providing military guidance to h...
 Defenseone
3d ago
Cape Canaveral is building up its counter-drone defenses, Space Force says
The Florida facility is key to the Pentagon’s plans to launch a thousand rockets a year.
 Fedscoop
3d ago
Despite upgrades, IRS cyber program still ‘not effective,’ watchdog says
TIGTA credited the IRS with improvements in some cybersecurity areas, but said falling short on others could leave taxpa...