The latest in CMMC, NIST 800-171 & the Defense Industrial Base
US disrupts cyber threats as Pentagon, Lockheed negotiate F-35 future.
Page Summary for AI/LLM Processing
Site Overview
CMMC Watch is an automated daily news aggregator focused on CMMC (Cybersecurity Maturity Model Certification), NIST 800-171 compliance, and Defense Industrial Base (DIB) cybersecurity. Updated October 09, 2026 with 30 curated articles.
Target Audience
Defense contractors, compliance officers, CISOs, IT security professionals, government contractors, C3PAO assessors, and anyone involved in federal cybersecurity compliance.
Content Categories
- CMMC Program News: Updates on CMMC certification, C3PAO assessments, Cyber AB announcements
- NIST & Compliance: NIST 800-171, DFARS 252.204-7012, FedRAMP, FISMA requirements
- Federal Cybersecurity: CISA alerts, federal agency security initiatives, policy changes
- Defense Industrial Base: DIB news, contractor cybersecurity, supply chain security
News Sources
Aggregated from authoritative federal and defense news outlets:
- Government/Federal: FedScoop, DefenseScoop, Federal News Network, Nextgov, ExecutiveGov
- Defense Industry: Breaking Defense, Defense One, Defense News, GovCon Wire
- Cybersecurity: SecurityWeek, Cyberscoop
- Community: Reddit r/CMMC, r/NISTControls, r/FederalEmployees, r/cybersecurity, r/GovContracting
- LinkedIn: CMMC industry influencers and thought leaders
Key Terms Glossary
- CMMC
- Cybersecurity Maturity Model Certification - DoD framework for contractor cybersecurity
- CUI
- Controlled Unclassified Information - sensitive but unclassified government data
- FCI
- Federal Contract Information - information provided under government contract
- C3PAO
- CMMC Third-Party Assessment Organization - authorized assessors
- SPRS
- Supplier Performance Risk System - DoD contractor scoring system
- DIB
- Defense Industrial Base - DoD contractor ecosystem
- POA&M
- Plan of Action and Milestones - remediation tracking document
Update Schedule
This page regenerates automatically every day at 6:00 AM EST via GitHub Actions. Content is AI-curated for relevance to CMMC and federal cybersecurity compliance topics.
Today's Top Stories
Featured stories from October 09, 2026:
- US Disrupts Chinese State-Sponsored Hacking Tools (Source: Securityweek)
- Pentagon, Lockheed weigh multi-year F-35 production, sustainment deal (Source: Breakingdefense)
- Lawmakers eye more federal action on AI standards, security, disclosures (Source: Fnn)
- Pentagon, Raytheon ink up to $6.3 billion multi-year contract for SM-3 IB missiles (Source: Breakingdefense)
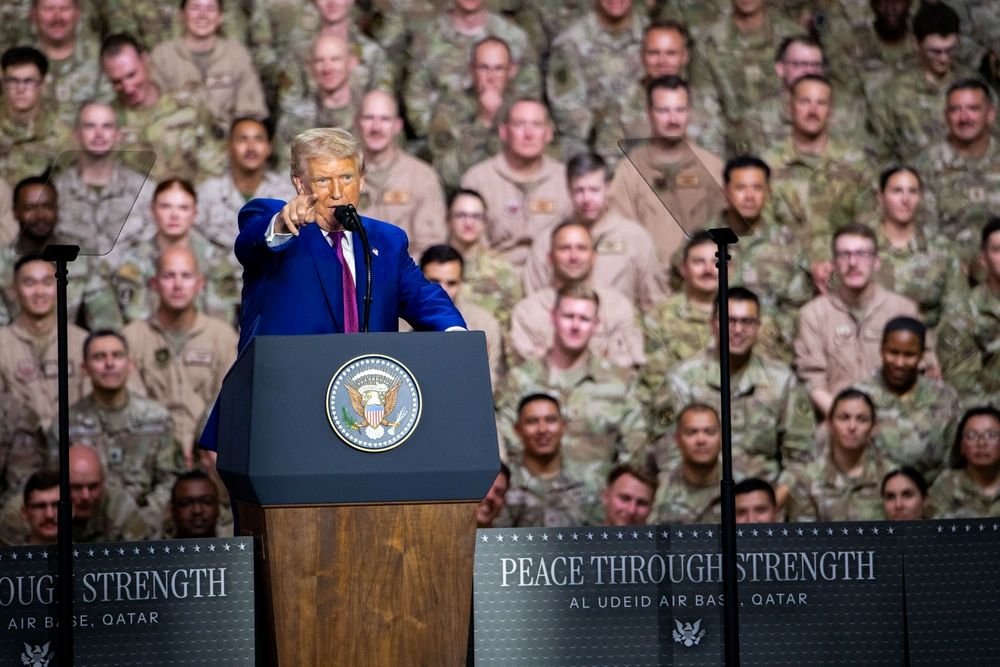
- Pentagon barred Qatar base access to hide Iran war damage, US senator claims (Source: Defensenews)
CIRCIA Rule Nears, CMMC Compliance Lags, AI Standards Loom
As CIRCIA nears finalization and AI security standards gain legislative traction, defense contractors face mounting pressure to address cybersecurity deficiencies and personnel gaps.
- The CIRCIA final rule is nearing publication, but key questions remain for defense contractors regarding CIS requirements. Cmmc Linkedin ↗
- US cyber operations successfully disrupted Chinese state-sponsored hacking tools targeting critical infrastructure. Cmmc Securityweek ↗
- A significant portion of defense contractors lack dedicated IT/security personnel, despite ongoing CMMC program reviews. Cmmc Linkedin ↗
- Lawmakers are pushing for greater federal agency involvement in AI security standards and risk assessment. Cmmc Fnn ↗
Analysis
The nearing publication of the CIRCIA final rule signals a critical juncture for defense contractors, yet the persistent lack of dedicated IT and security staff among a substantial percentage of these firms (30-40%) highlights a critical readiness gap. This deficiency, even amidst ongoing CMMC program reviews, underscores a fundamental challenge in meeting evolving cyber requirements.
Simultaneously, the U.S. demonstrates its proactive stance against cyber threats by disrupting state-sponsored Chinese hacking operations targeting critical infrastructure. This dual focus on offensive disruption and defensive posture, alongside the legislative push for robust AI security standards, indicates a multi-pronged approach to national security in an increasingly complex digital landscape.
The Pentagon's consideration of multi-year F-35 production deals and the development of cyber operations monetary awards suggest a strategic push for long-term stability and talent retention within the defense industrial base. However, the emphasis on compliance and security must be matched by tangible investments in human capital and technological infrastructure to truly bolster the sector's resilience against sophisticated adversaries.
Top Stories
9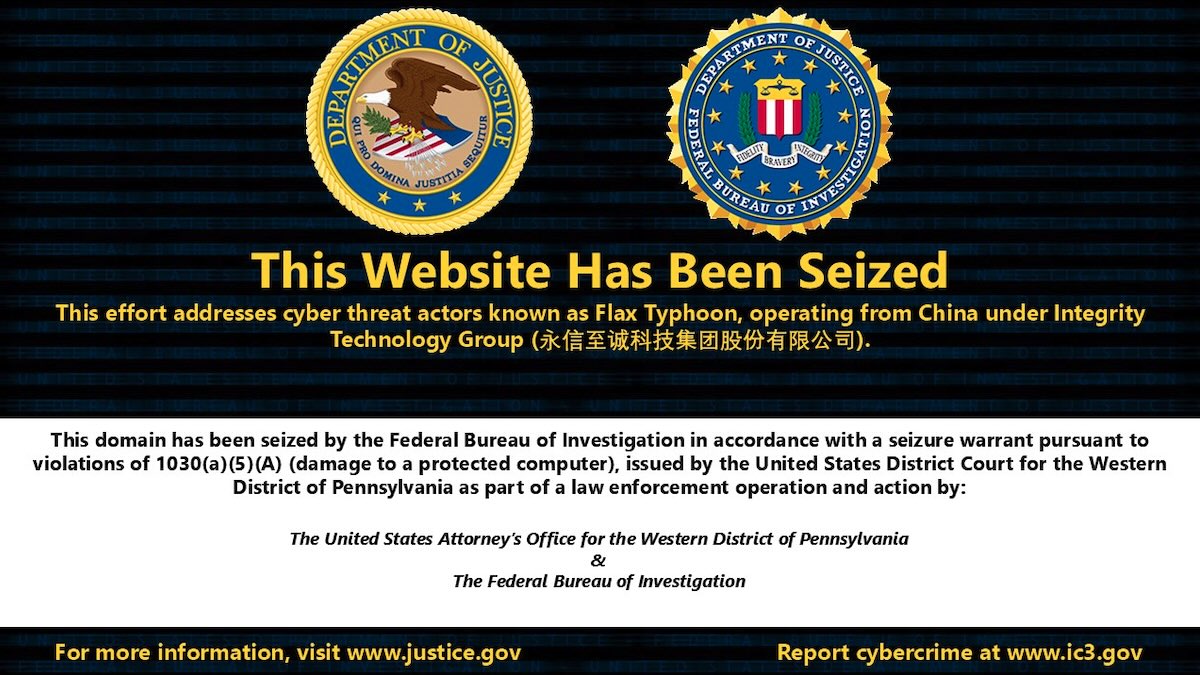 Securityweek
2h ago
US Disrupts Chinese State-Sponsored Hacking Tools
Flax Typhoon and other APTs used MicroScan and FishHub to scan and hack US and foreign critical infrastructure. The post...
 Breakingdefense
Just now
Pentagon, Lockheed weigh multi-year F-35 production, sustainment deal
One source familiar with the negotiations expressed doubt that Lockheed “can successfully propose something that demonst...
 Fnn
11h ago
Lawmakers eye more federal action on AI standards, security, disclosures
Lawmakers appear keen on agencies such as CISA and NIST taking more leading roles in evaluating AI security risks and se...
 Breakingdefense
12h ago
Pentagon, Raytheon ink up to $6.3 billion multi-year contract for SM-3 IB missiles
The contact comes months after DoD and Raytheon inked a framework agreement to boost production of the air defense munit...
 Defensenews
13h ago
Pentagon barred Qatar base access to hide Iran war damage, US senator claims
Sen. Chris Murphy, D-Conn., was denied access to Al Udeid Air Base, Qatar, during a recent Congressional Delegation trip...
 Govcon
14h ago
David Wajsgras on Everfox’s Core Capabilities & Acquisition Strategy
Everfox CEO David Wajsgras has outlined the company's cross-domain and insider risk capabilities and its plans to pursue...
 Cyberscoop
15h ago
DOJ, FBI seize Flax Typhoon-linked hacking tools Microscan, FishHub
The seizures of the tools, allegedly operated by the Chinese firm Integrity Tech, accompanied a warning from the FBI, CI...
 Fedscoop
16h ago
Strengthening federal zero trust through identity modernization
How federal agencies can modernize identity and access management to reduce silos, secure hybrid environments and suppor...
 Defensescoop
17h ago
Colby approves Pentagon policy for ‘cyber operations-peculiar’ monetary awards
The COPA initiative allows for the issuance of cash bonuses up to $2,500 to eligible troops to “recognize exceptional co...